Four months ago, I left my job as a Threat Researcher at Microsoft to go full-time on SecurityBreak.
In this edition, I want to talk about what I am building and give you some insight into what happens behind the scenes.
The past few months
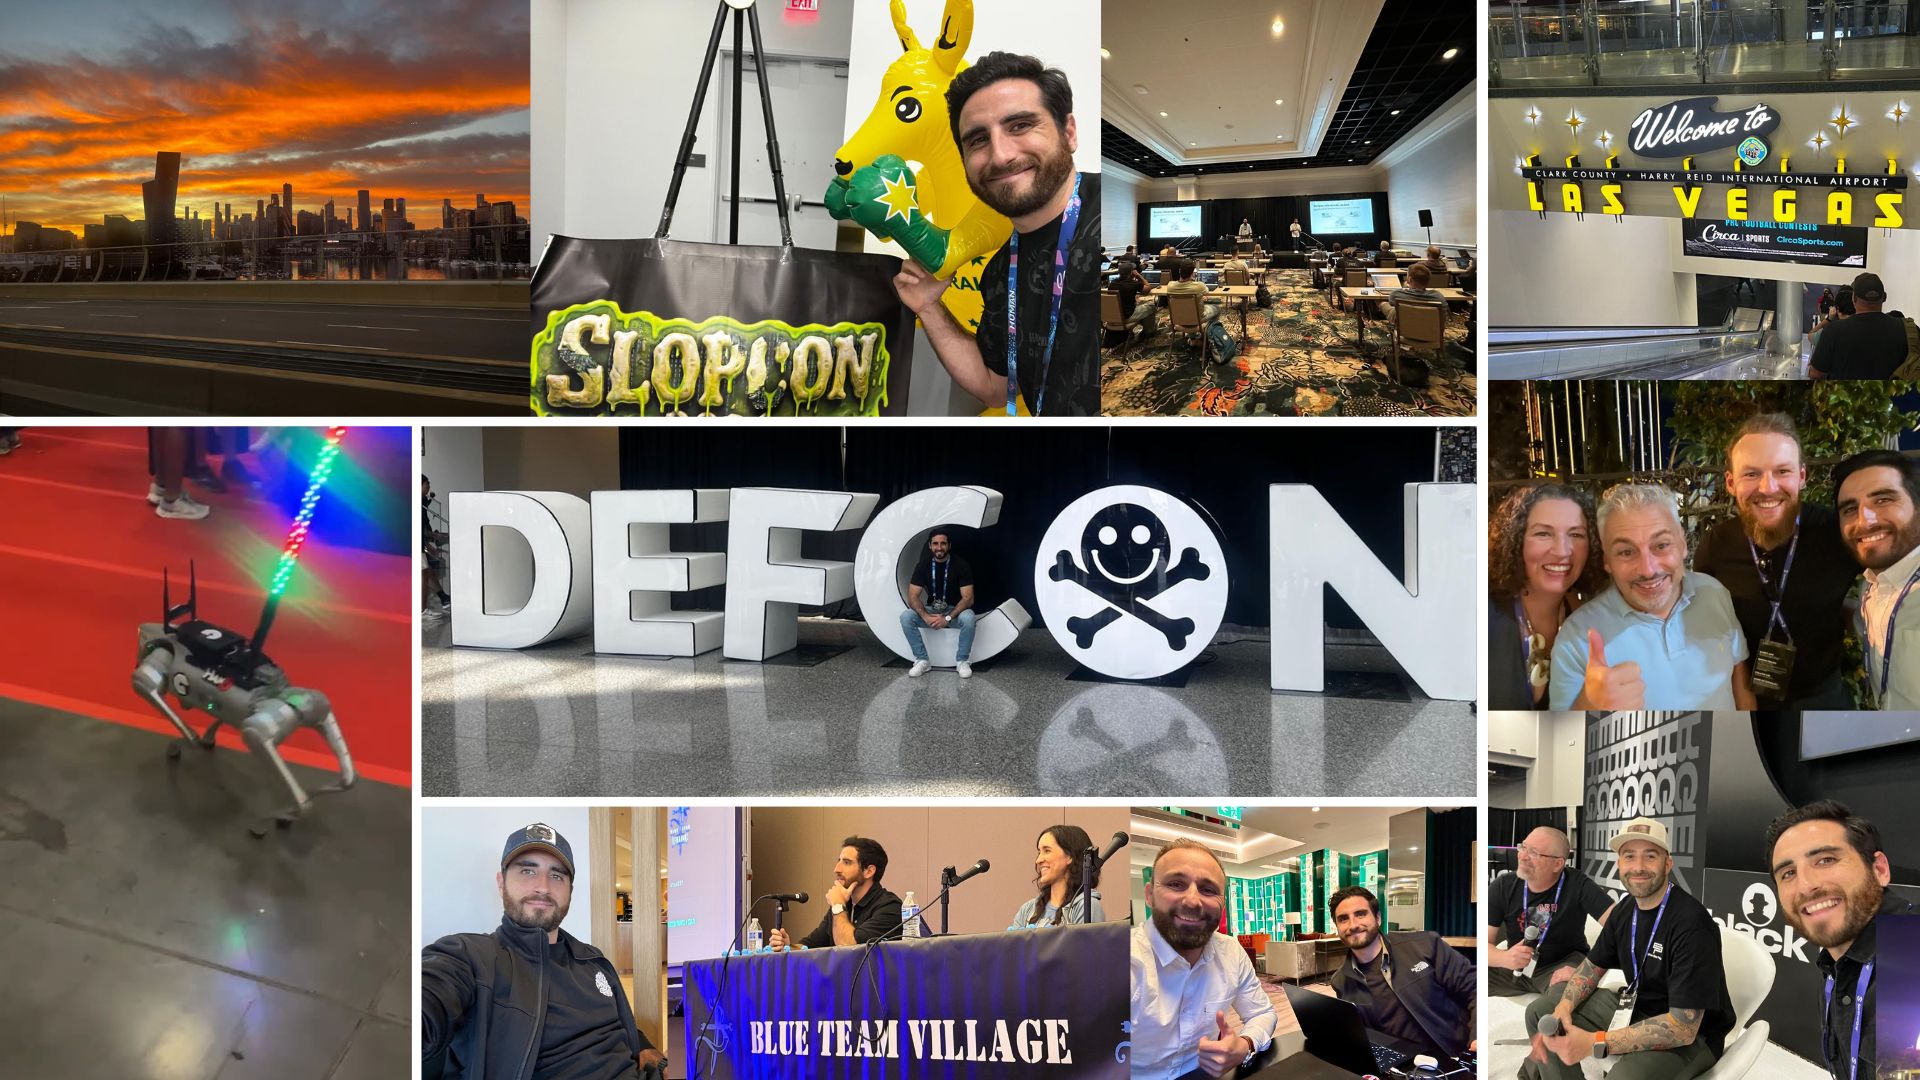
Over the past few months, I have spent a lot of time talking to people about AI security. I went to Las Vegas for Black Hat and DEF CON, gave multiple presentations on AI security, and taught my training on AI for CTI.
During my 15+ years in the security industry, I focused on tracking threat actors and working on breaches across the world, from cybercrime to high-stakes nation-state espionage.
I have always believed that good defense comes from the battlefield, from a deep understanding of how threat actors operate.
Since the early days of modern AI, I have spent a lot of time understanding how defenders could use this technology to operate faster and better. I saw the value early and if I could see it, threat actors could too...
That is why I started to apply what I had learned from more than a decade of threat intelligence to the AI field. I was convinced that threat actors would take advantage of AI sooner rather than later.
From early experiments with malware LLMs and disinformation to offensive agentic workflows, I tracked the threat to understand how attackers use AI but also how they target AI systems themselves.
A new attack surface
Today, organisations and governments across the world rapidly deploy AI into production. This introduces a new ecosystem: LLMs, agents, MCP servers, skills, workflows, AI assistants...
But this new ecosystem also introduces a new attack surface, with its own threats and security challenges.
I founded SecurityBreak to focus on AI threats.
We provide intelligence to the AI ecosystem, track threat actors and monitor how the AI threat space evolves.
But that is only one part of what we do.
From threat intelligence to NovaHunting
AI Threat Intelligence gives us a deep understanding of the threats that target AI. To operationalise that intelligence, we are also building NovaHunting, a platform designed to give you visibility across your AI ecosystem.
We want security teams to understand what their AI agents are doing, which tools they use, what MCP servers or skills they interact with, what data they access and what happens across a full session.
AI agents, MCP servers, skills, AI assistants, workflows...
Our goal is to give you visibility across your AI systems without locking you into one vendor or environment.
Why threat intelligence first?
I know there are already many startups working on AI security.
Our difference is that we are building from threat intelligence first.
I believe strong defense starts with a deep understanding of the threat.
We are looking for design partners
We are still early, and we are looking for design partners who already deploy AI agents, assistants, or workflows and need better visibility into what they are doing.
By joining us at this stage, we can help you build your AI Security practice, and you can be part of our roadmap.
If that sounds like your organisation, you can reach out to us at contact@securitybreak.io. I would be happy to show you NovaHunting and hear about the problems your team is facing.
Thomas
